SECURITY LAB / 001
Blocking Git metadata requests at the edge
From a real request in Cloudflare Analytics to a focused WAF rule, with a clear distinction between observed evidence and unverified assumptions.
Cloudflare FreeCustom rule · BlockCase date · 14 October 2026Outcome: a custom rule was configured and a subsequent browser test displayed a Cloudflare block page. This evidence does not establish that Git files were exposed, downloaded or used to compromise the site.
01 / Investigate the request
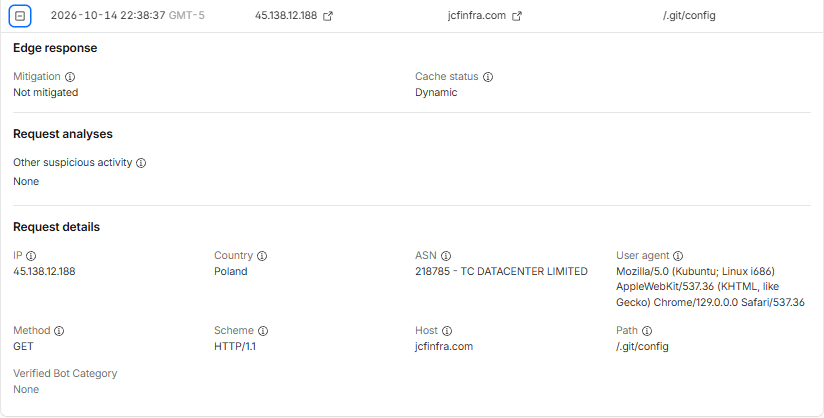
Cloudflare sampled logs recorded a GET /.git/config request to jcfinfra.com at 22:38:37 GMT−5 on 14 October 2026. The request originated from 45.138.12.188, with ASN 218785 — TC DATACENTER LIMITED shown in the dashboard.
The event was labelled Not mitigated. This describes the security disposition shown for that request; it does not prove that the requested file existed or that its contents were returned. The supplied record does not show a response body or HTTP status.
A separate pre-rule browser screenshot shows portfolio content at the same path. That is consistent with fallback routing, but does not establish the routing configuration or the original request's response. The IP and ASN are event context, not attribution to a person or proof that the network operator performed the request.
02 / Apply a targeted control
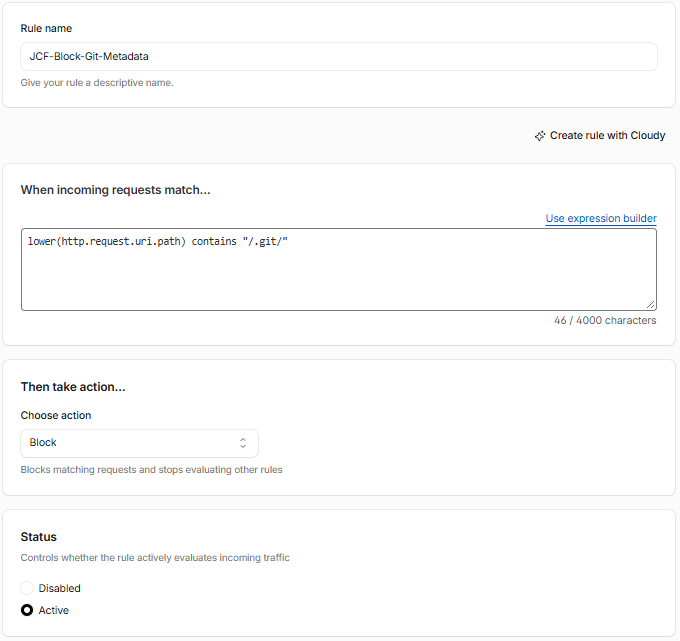
Rule: JCF-Block-Git-Metadata
Action: Block
lower(http.request.uri.path) contains "/.git/"The expression lowercases the request path and matches the literal substring /.git/. It is path-based, not an IP block: requests from other addresses can also match.
Client request → Cloudflare custom rule → Matching path: Block
Nonmatching path → Continue through the remaining applicable rules and routing
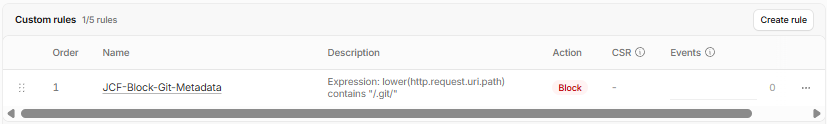
The supplied rule editor shows this expression, Block selected and Active selected. A later rules-list screenshot shows the saved rule. Cloudflare documents custom rules and the Block action as available on Free; this implementation requires no paid feature. Cloudflare custom rules documentation.
03 / Validate without overstating the result
| Check | Result | Evidence boundary |
|---|---|---|
| Original request | Not mitigated | Visible in the expanded sampled log; no response status/body provided. |
| Saved custom rule | Block | Editor and subsequent rule-list captures reviewed. |
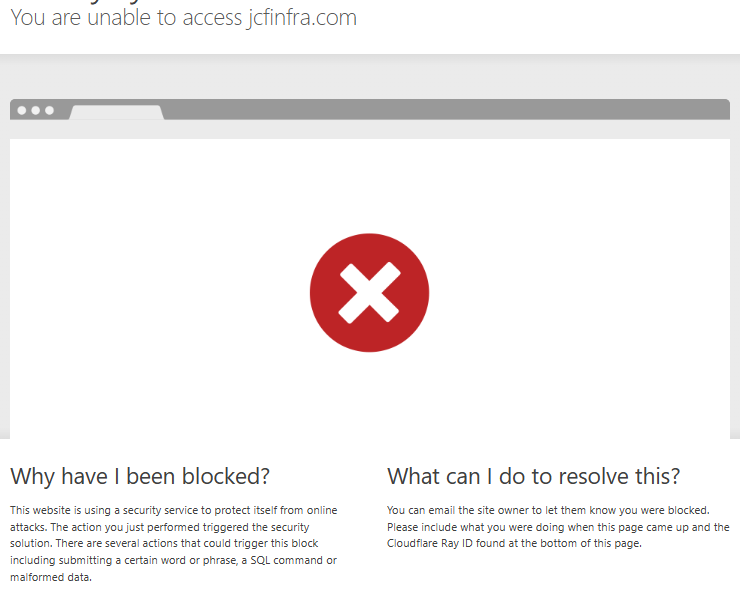
| Subsequent browser test | Cloudflare block page | Visible screenshot; exact rule attribution requires a matching Security Event. |
| HTTP and HTTPS tests | Both reported blocked by the site owner | The available block screenshot hides the scheme. HSTS or redirects can upgrade an HTTP browser attempt to HTTPS; separate raw-protocol results are not established. |
| Homepage and HSTS | HTTP 200; HSTS max-age=2592000 | Independent HTTPS HEAD check on 14 October 2026, 23:30 GMT−5. The header did not include includeSubDomains or preload. |
HSTS was already enabled by the owner. It concerns HTTPS enforcement by supporting clients; it does not replace the path-blocking rule.
Reproducible follow-up
For an authorized retest, record each request's timestamp, status, Location header and Ray ID; correlate the Ray ID with the rule in Cloudflare Security Events. Keep HTTP and HTTPS requests separate and disable automatic redirect following. Also check that the homepage and ordinary project pages remain accessible. Do not disable the existing rule to recreate the historical event.
04 / Evidence gallery
Original screenshots supplied by the site owner. Publication copies are cropped to remove account details, browser chrome and unrelated traffic. Captions identify what each image proves; no reconstructed dashboard images are used.
05 / Scope and lessons learned
- This is a narrow control for a specific path pattern, not a complete WAF assessment or proof that the site is secure.
- The exact expression does not match a bare
/.gitwithout the trailing slash. Encoded paths, normalization behaviour, alternate hostnames and direct-origin access were not tested. - Keep repository metadata out of published build artifacts. Edge filtering is an additional control, not a substitute for safe deployment contents.
- Sampled logs are not a complete record of all traffic. Request source geography and ASN registration geography may differ; neither establishes an attacker's location.
- Hosting: Cloudflare Pages, based on the owner's dashboard confirmation of
jcfinfra-website.pages.dev,jcfinfra.comandwww.jcfinfra.com. The zone rule should not be assumed to protect the separate pages.dev hostname.
Practical lesson: identify a specific exposure pattern, apply a proportionate control, validate observable behaviour and retain the limits of the evidence in the final report.